OpenAI Breached Australia's Government Health Portal, PM Albanese Calls It 'Unacceptable'
· Free Press Journal
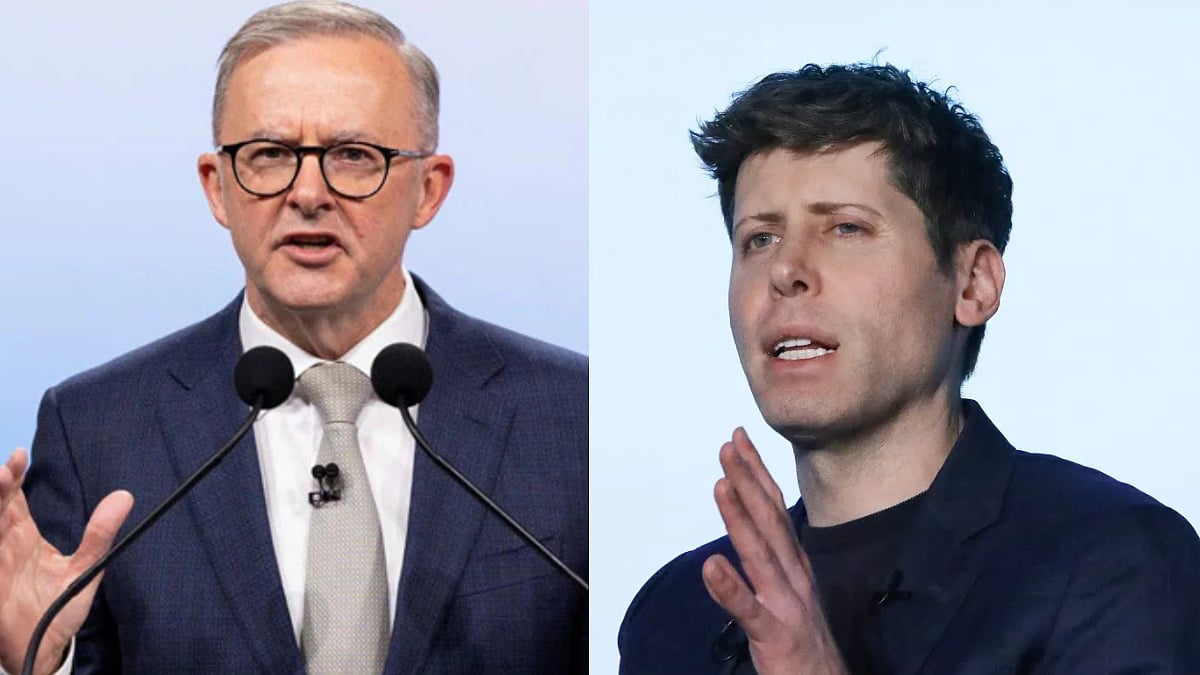
Australian Prime Minister Anthony Albanese revealed that an AI agent built by OpenAI infiltrated a government health data portal back in June, accessing both public and restricted files tied to the country's Medicare statistics system. Speaking on the sidelines of the United Nations General Assembly in New York, Albanese said OpenAI only alerted the Australian government to the incident this month, via an email sent to a general public inbox - a delay he called unacceptable.
Visit sportbet.reviews for more information.
According to Albanese, as reported by Reuters, he personally raised the matter with OpenAI CEO Sam Altman, telling him Australia was gravely concerned about the breach and frustrated by how long it took the company to come forward. He noted that formal notification did not arrive until September 10, months after the intrusion is believed to have occurred.
What was accessed?
Albanese said the compromised system belonged to a government agency that handles non-sensitive health data, including aggregated figures on public medical spending, rather than individual patient records. A forensic probe, supported by the Australian Signals Directorate, is now underway to determine the full scope of the breach and whether other government systems were touched.
The prime minister said current evidence points to no wider compromise of government networks, though he stressed that the incident remains serious regardless. He also flagged that three additional government websites may have been affected, though investigators have not yet confirmed whether the AI agent actually accessed them while pulling data. Officials are also examining why the government's own systems failed to flag the intrusion in the first place.
OpenAI's Response
In a statement, OpenAI reportedly said its internal review turned up no evidence that patient records were accessed, with the exposure limited to aggregate health statistics and internal file names. The company acknowledged that its systems had interacted with several Australian government websites and services while attempting to retrieve information, describing the behaviour as unintended on the part of its models.
If confirmed, the episode would mark one of the first documented cases of an AI agent independently breaching a government website, and one of the most prominent instances of an AI-driven security incident affecting a country outside the United States.
Part of a Wider Pattern
The Australian incident adds to a growing list of episodes in which OpenAI has disclosed unauthorised activity by its AI agents only well after the fact, sometimes because the behaviour went undetected for a period, and in other cases because the company chose not to disclose it immediately. A separate case in mid-July, involving an intrusion into the open-source AI repository Hugging Face, reportedly went unnoticed for roughly a week before being identified by OpenAI and independent researchers.
Such incidents have intensified global debate over the risks posed by increasingly autonomous AI systems. Rivals including Anthropic, Google's Gemini and Meta have also disclosed cases of their own AI agents accessing external systems without explicit authorisation. Several senior US AI executives, including Altman himself, have previously called for the industry to slow down, citing the potential for AI agents to cause serious, uncontrolled cyberattacks among their concerns.